Cybersecurity & DefenseFLAGSHIP
Virtual CISO (vCISO) Services
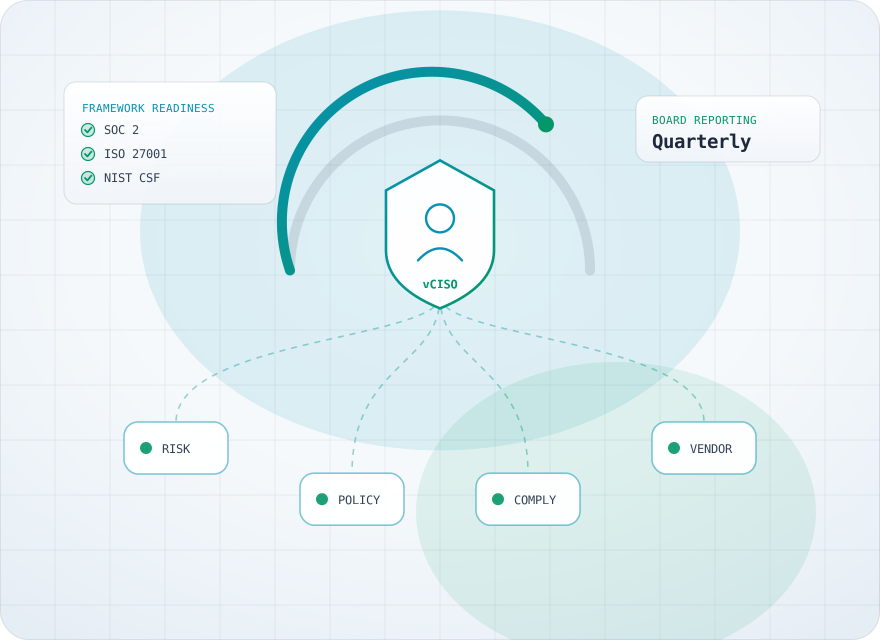
Executive-level security leadership without the executive hire. Your vCISO owns the strategy, the risk register, the policies and the board conversation — operating as an extension of your internal team, backed by a project team that implements the work rather than just recommending it.
Do You Need One?
Four signals it's time for security leadership
Most organizations don't decide to hire a CISO — they discover they needed one. These are the moments that usually trigger the conversation.
No experienced security leader
Security decisions are landing on IT, engineering or the CFO — people with day jobs and no mandate to own risk.
Customer security questionnaires are stalling deals
Enterprise prospects send assessments your team can't answer confidently, and procurement slows to a crawl.
A framework is now mandatory
SOC 2, ISO 27001, HIPAA or PCI DSS has moved from 'someday' to a contractual or regulatory requirement.
Nobody owns incident preparedness
There's no tested response plan, no defined escalation path, and no one accountable when something goes wrong at 2am.
What's Included
Nine disciplines, one accountable leader
Your engagement draws on whichever of these your program needs — sequenced by the roadmap, not sold as separate projects.
IT Security Risk Assessment
Cybersecurity Maturity Assessment
Security Strategy & Leadership
Business Continuity & Disaster Recovery
IT Security Policy Drafting
Vendor Security Management
Security Control Implementation
Cybersecurity Training & Awareness
Compliance Validation
Engagement Model
An extension of your team — not a report on a shelf
Your vCISO is a named senior practitioner who learns your business, attends your leadership meetings and stays accountable for the program between them. Behind them sits a dedicated project team that implements the improvements — so the roadmap actually moves.
Fractional cost
A fraction of a full-time CISO salary, scoped to the leadership hours your organization actually needs.
Flexible commitment
Scale hours up during an audit or incident, down during steady state — the engagement flexes with your year.
Board-ready communication
Quarterly reporting written for directors and investors, with maturity scoring they can track over time.
How It Runs
- 01
Discover
We assess your current posture, business risk profile, regulatory obligations and existing controls — establishing the baseline everything else is measured against.
- 02
Prioritize
Findings become a ranked roadmap: what to fix now, what to schedule, and what to accept — each with effort, cost and risk-reduction attached.
- 03
Execute
Your vCISO drives the program forward with a dedicated project team implementing policies, controls and training on an agreed cadence.
- 04
Report & Mature
Quarterly board-ready reporting, updated maturity scoring and a rolling roadmap keep the program advancing rather than plateauing after the first audit.
Common Questions
What clients ask before they start
What exactly is a virtual CISO?+
A virtual CISO (vCISO) is an experienced security executive who serves as your organization's security leader on a fractional, ongoing basis. You get the strategic judgment, framework fluency and board credibility of a Chief Information Security Officer — sized and priced to your organization, without the full-time executive hire.
How is an engagement structured?+
Engagements are customized to your needs and typically combine a set number of vCISO leadership hours per month with a supporting project team that implements the work. Most clients start with an assessment phase, then move to a recurring retainer that advances the roadmap quarter by quarter.
Can you get us to ISO 27001 or SOC 2 certification?+
Yes. We run the full path: gap assessment against the standard, remediation planning, policy and control implementation, evidence collection, internal audit, and liaison with your certification body or audit firm through to report or certificate.
Do you help with incident preparedness?+
We build and test the plan before you need it — incident response playbooks, defined escalation paths and roles, and tabletop exercises that rehearse your leadership team through a realistic breach scenario. If an incident does occur, our Threat Detection & Response practice provides the containment and forensics capability.
How is this different from hiring a security consultant?+
A consultant delivers a project and leaves. A vCISO owns your security program continuously — accountable for the roadmap, present in leadership conversations, and available when a customer questionnaire, an auditor or an incident needs an authoritative answer.
Put a security executive behind your business
Start with a maturity assessment — we'll show you exactly where your program stands and what leadership it needs next.